 Nederlands
 English
You share business data. That data has to be handled with care.
To analyse marketing performance, Datafy uses information about media spend and commercial results. That is sensitive business data. That is why it has to be clear where the data is stored, who has access to it and which agreements apply to how it is used.
Clear agreements on how data is used
European hosting
All data is stored in data centres within the EU and does not leave the EU. No transfer to countries outside the European Economic Area.
Data isolation per customer
Each customer has its own, separated database environment. Your data is never mixed with that of other customers and never used to improve anyone else's models.
Encrypted, in transit and at rest
Traffic runs exclusively over TLS; stored data is encrypted. Access to production systems is limited to authorised engineers.
GDPR as the starting point
Datafy works with aggregated media and sales data, not personal profiles. A data processing agreement (DPA) is a standard part of every contract.
Access management & logging
Roles and permissions per user, and logging of access. You decide who in your organisation sees what.
No data trading
Your data is not sold, not shared with third parties and not used for benchmarks without your explicit consent. Full stop.
Every decision and every AI action: recorded
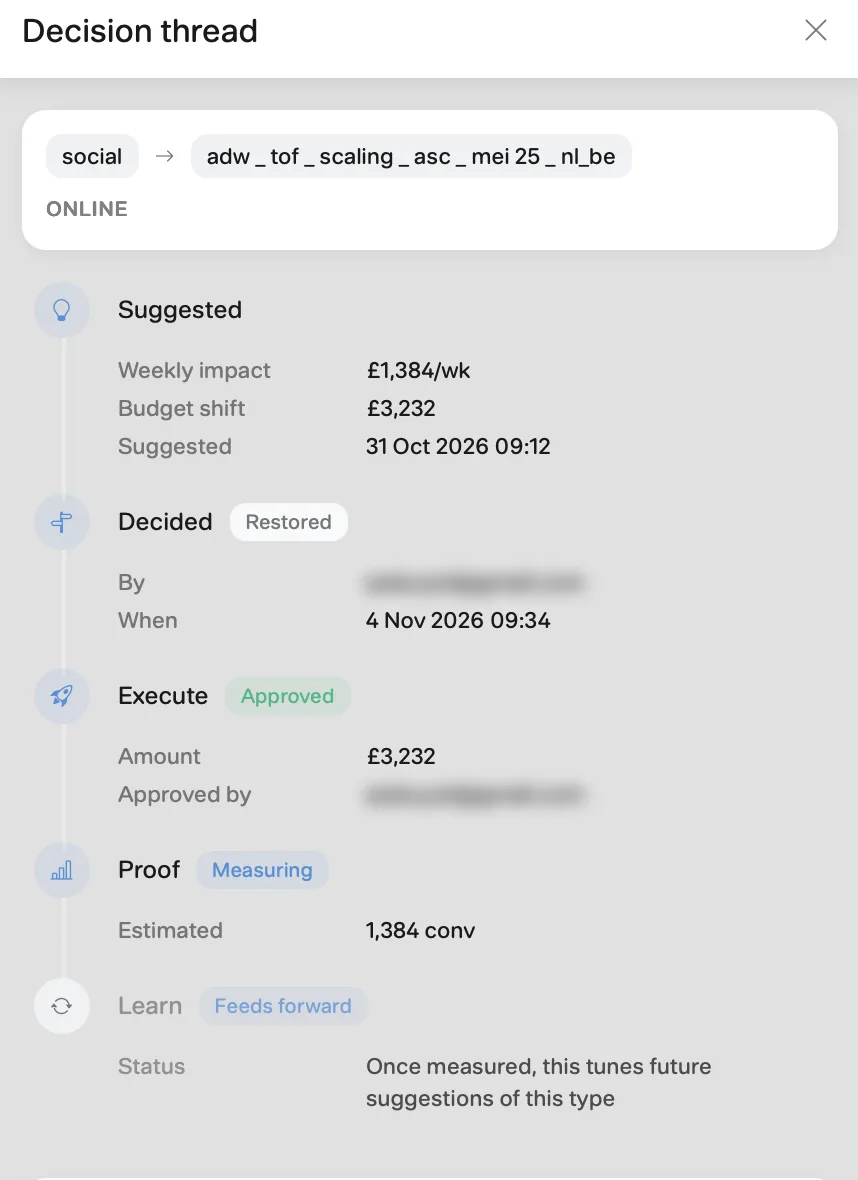
From recommendation to measured effect, per decision
Every decision has its own thread: who decided what, when, on the basis of which recommendation, and what it actually delivered 2 to 4 weeks later. The full decision log is searchable, recoverable and exportable. No after-the-fact debates about who changed what and why.
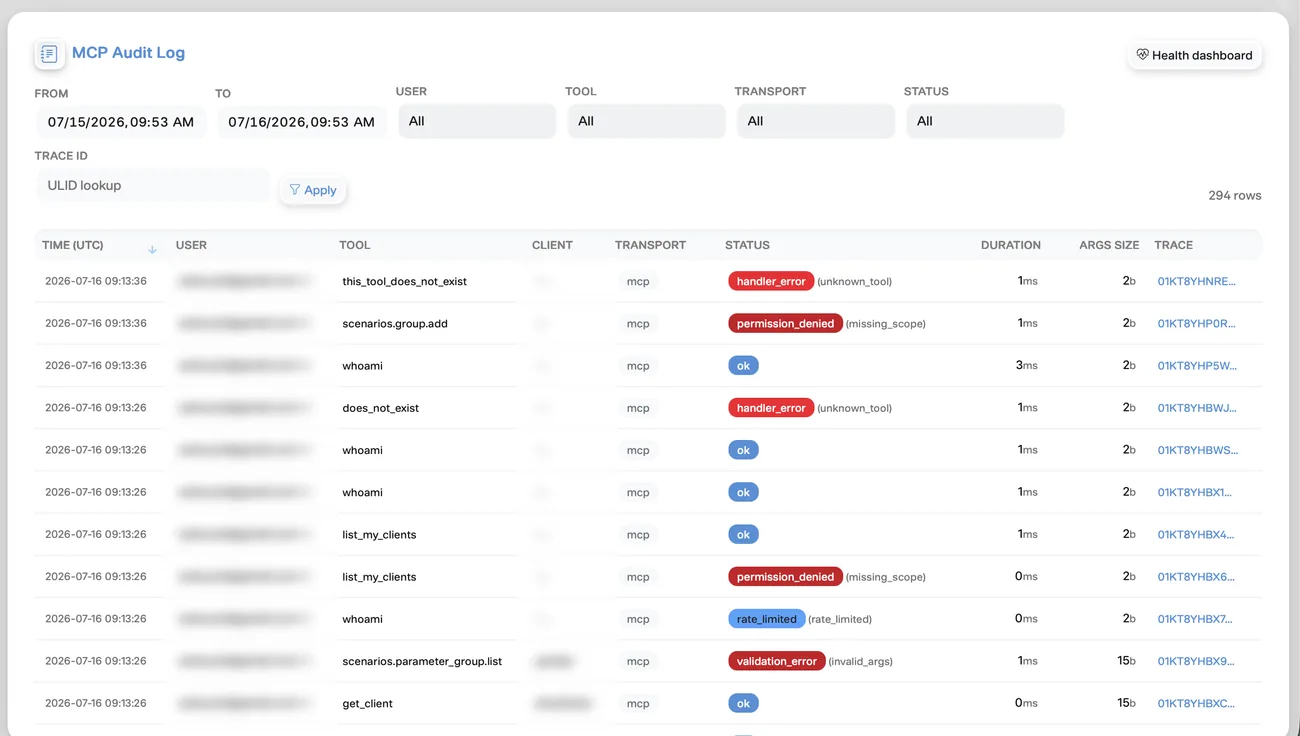
The AI assistant leaves a full trail too
Every action of the AI assistant (every query, every recommendation, every change) is logged with user, timestamp, status and trace ID. Arguments are stored as a hash (no PII), with 365 days retention. Your security team can inspect the log itself; denied actions are just as visible as executed ones.
Insight into access and changes
For organisations it is important to know which employees can view or change data and how access is recorded. The same applies to the traceability of analyses and of the decisions that were taken. Ask us for the current documentation for your security and privacy assessment.
Architecture description
How the environments are separated, where data is stored and how the data flow runs, from delivery to model.
Data processing agreement
Standard DPA template including an overview of sub-processors and retention periods.
Security questionnaires
We complete your own vendor assessment (SIG, CAIQ or custom) within five working days.
Answering security questions before we start working together
We are happy to discuss which data is needed, which data is specifically not needed and which technical and contractual measures are in place.